Sample report
Sample penetration test report
This is the report format we send after a test. The client, Harbor Notes, is fictional. Its app, its people and all nine findings are sample data.
Download the sample report (PDF, 11 pages, 300 KB)
What is in the report
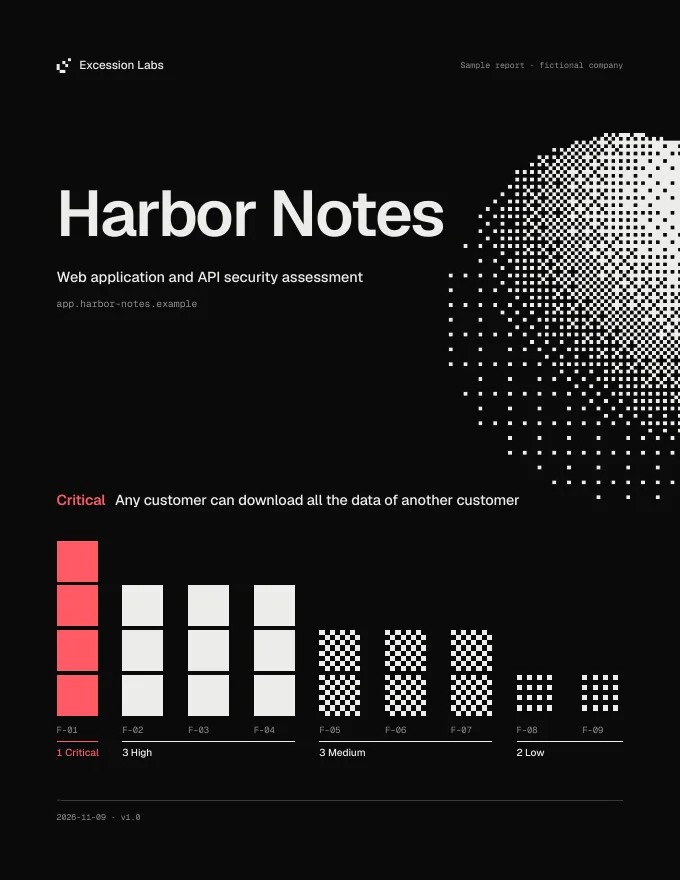
- Cover: the target, the worst finding in one line, and a count of findings by severity.
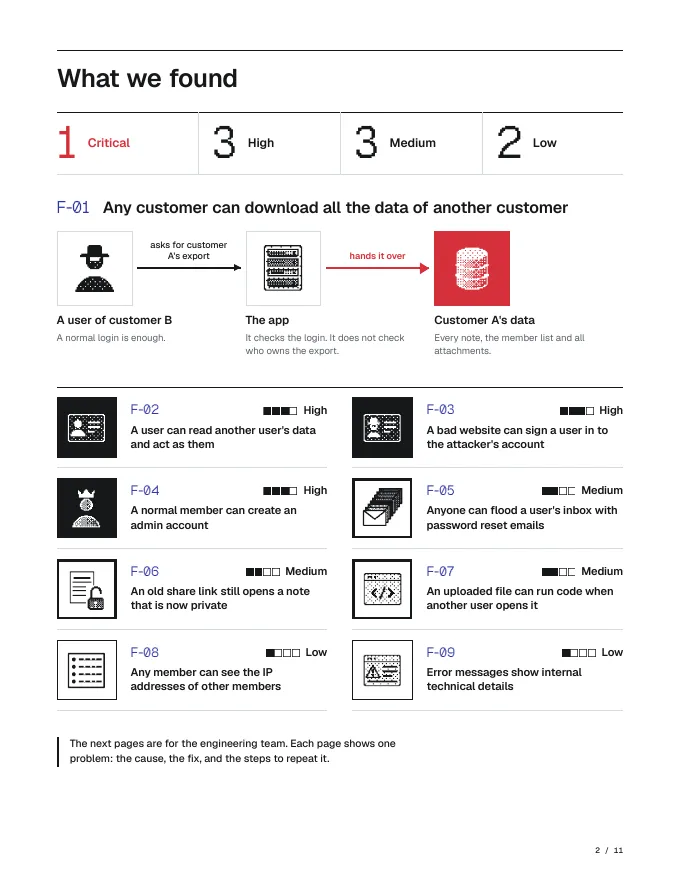
- What we found: one page in plain words. It shows the most serious finding as a picture, then lists every other finding by title and severity.
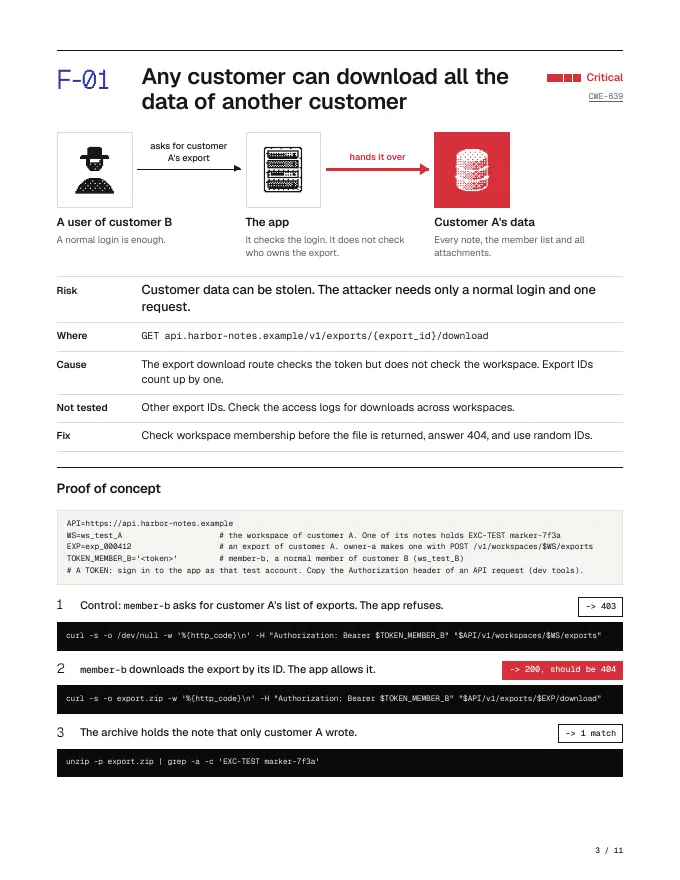
- One page for each finding: a picture of the attack, then rows for Risk, Where, Cause and Fix, then proof-of-concept steps with the commands and the result each step should give.
Who each part is for
The first two pages are for a reader who is not technical, such as a founder or a manager. They show what is most serious and which data an attacker could reach.
The finding pages are for the engineer who fixes the problem. The routes, the cause, the fix and the proof-of-concept steps are real text in the PDF, so the engineer can copy them or give the file to a coding tool.
Pages from the report
Single findings from our research notes
Three findings from our research notes, each written up as a one-page sample report:
- IDOR: one user reads another user's records (PDF)
- SSRF: the server fetches an internal address (PDF)
- SQL injection: input changes a database query (PDF)
To read how a test runs and what we test, see Application security assessment.